What it is
Why it exists
Scope
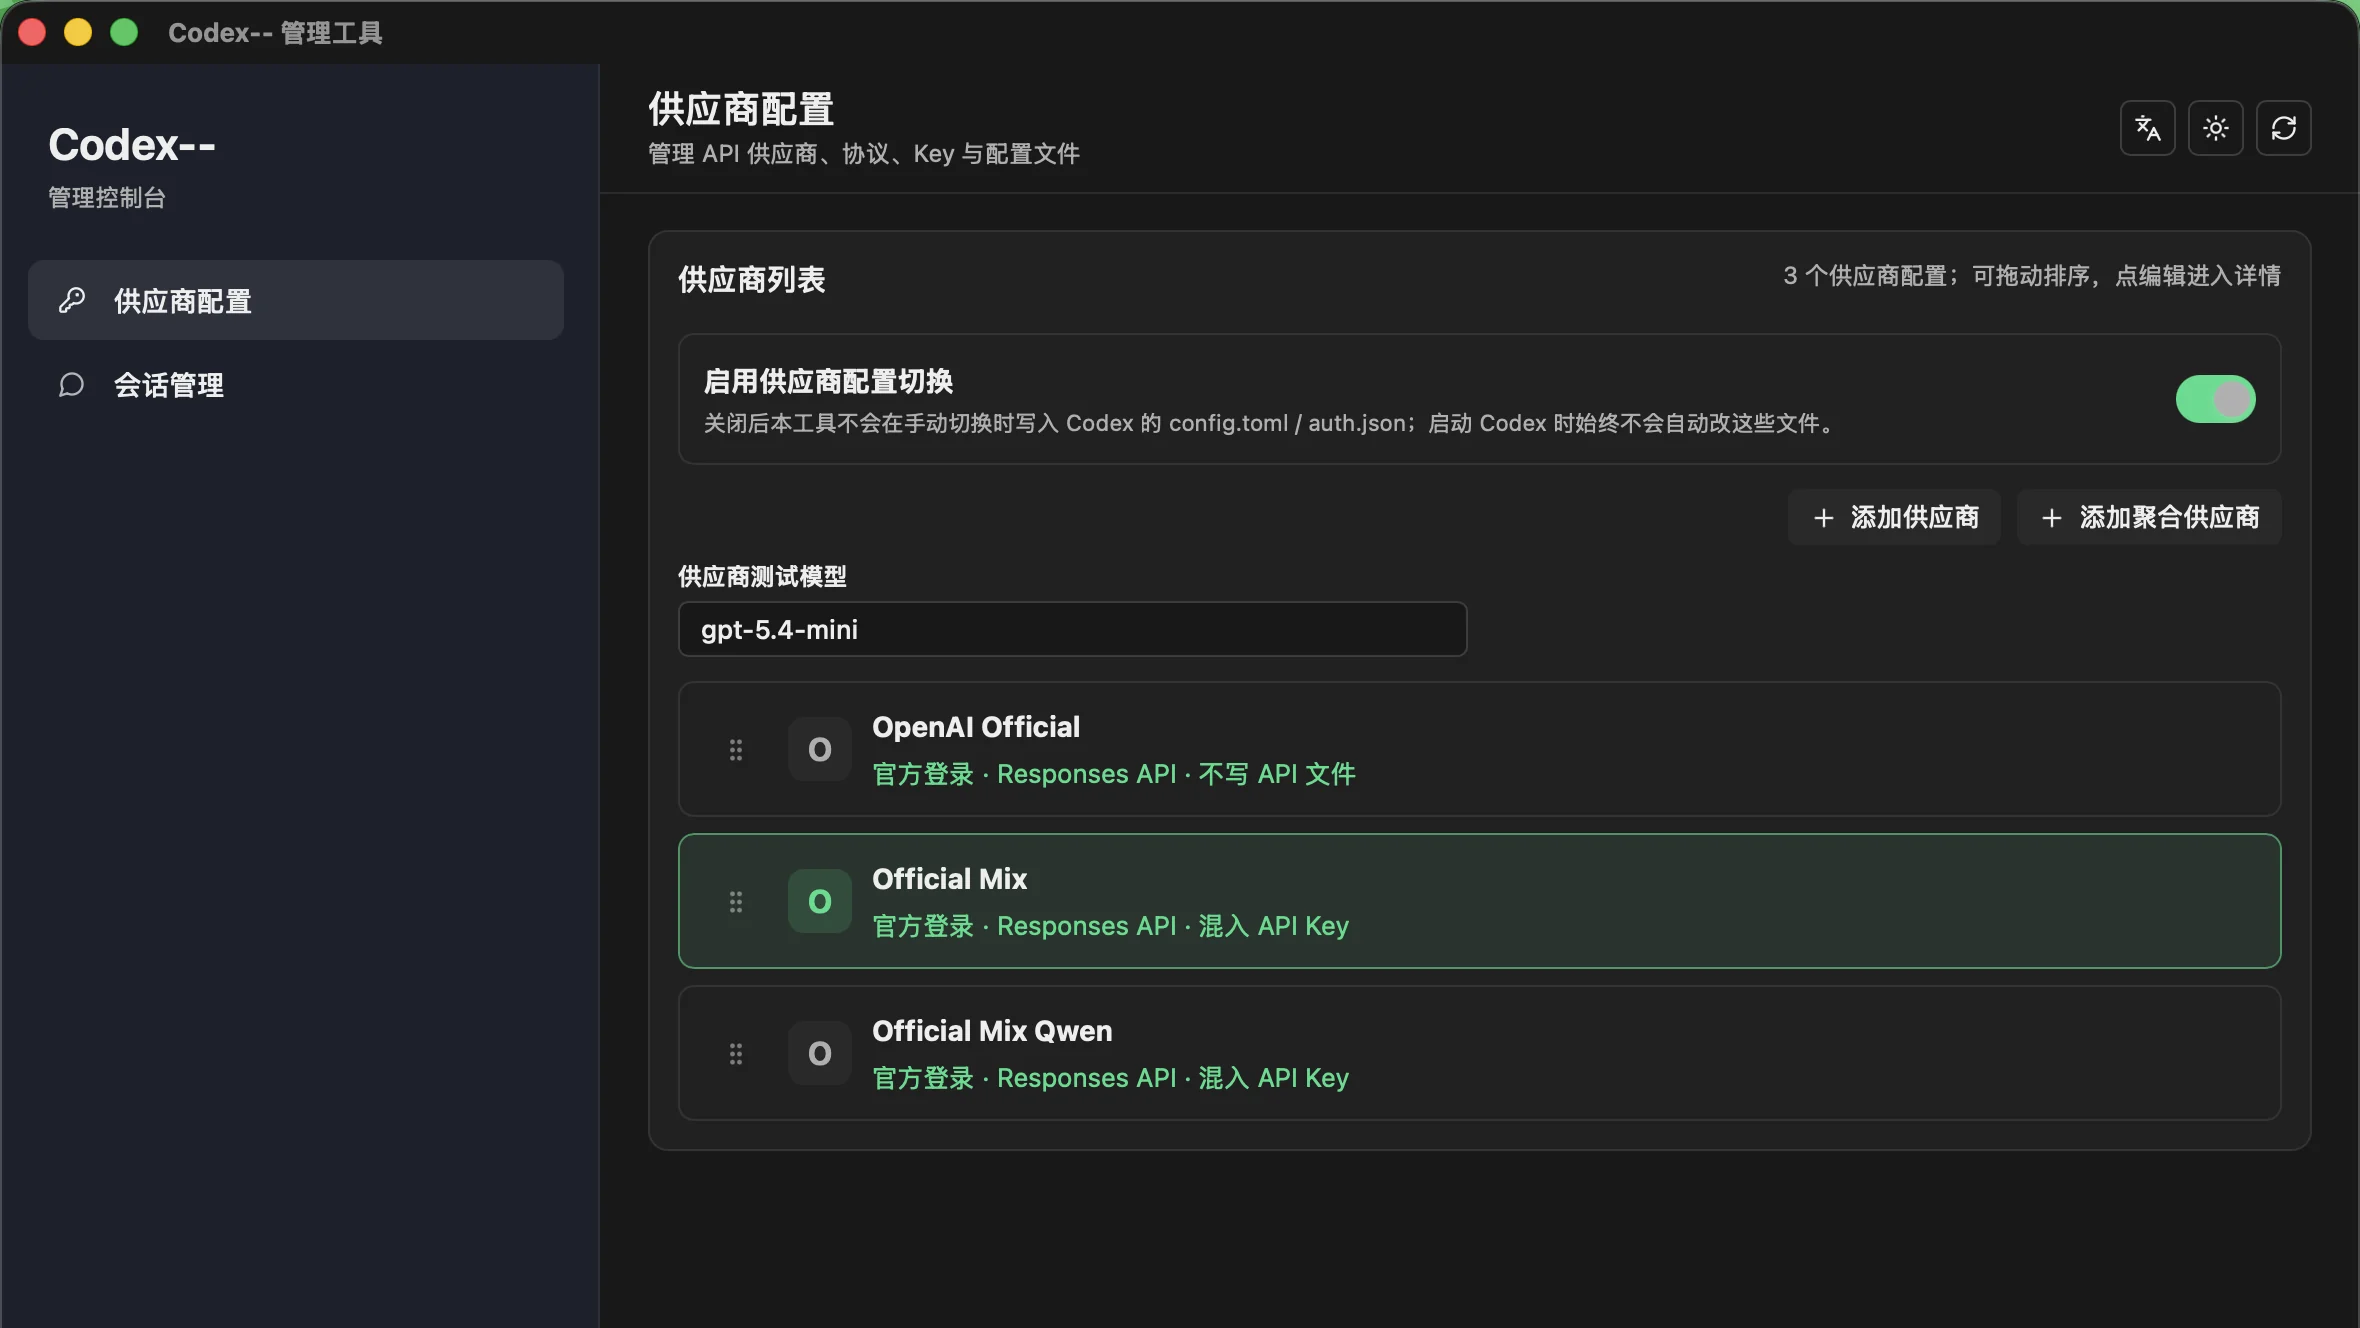
- Relay provider profiles with OAuth and API key combinations
- Native official, official plus custom, custom-only, and external catalog modes
- Official-client-owned auth.json with no provider-driven writes
- Recoverable Context-protected transactions for settings, config.toml, and catalogs
- Active and archived session pagination
- Native archive and restore with postcondition checks
- Read-only active-session provider compatibility checks
- Environment conflict diagnostics
Distribution
Links
这是什么
为什么需要它
范围
- OAuth 与 API Key 混合的中转供应商 profile
- 官方原生、官方加自定义、仅自定义与外部目录模式
- auth.json 由官方客户端管理,供应商操作不写入
- settings、config.toml 与目录的可恢复 Context 保护事务
- 活动与归档会话分页
- 带后置条件检查的原生归档和恢复
- 只读的活动会话供应商兼容性检查
- 环境变量冲突诊断